Security
Safe by default, and you can check it yourself.
A lot of what goes wrong in AI-built apps is the same mistake: the screen hides data, but the server hands it to anyone who asks. make27 is built so that can't be the only lock on the door.
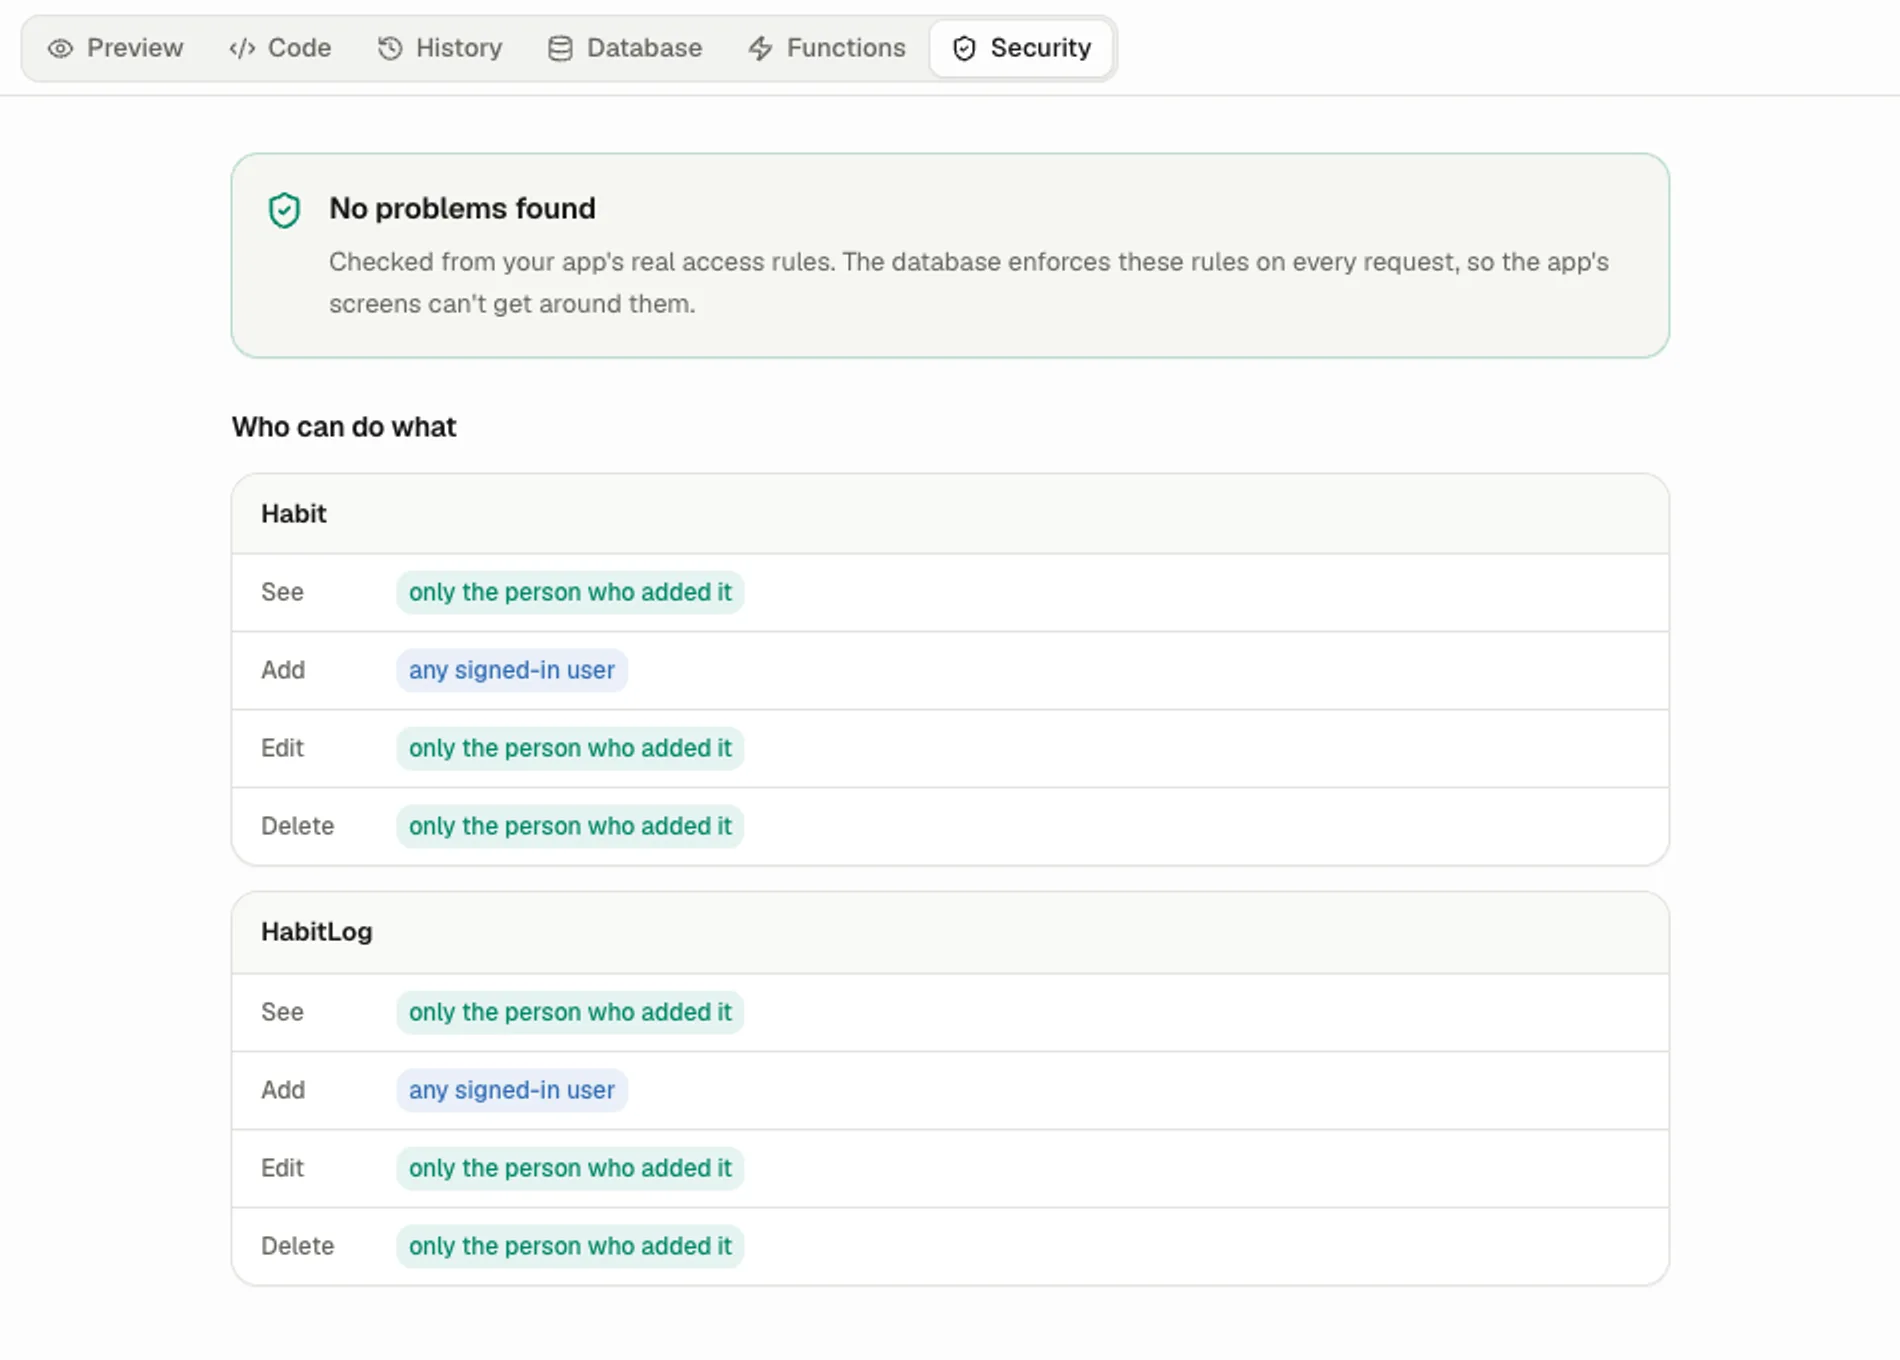
Rules checked by the server
Who can see, add, edit or delete each kind of record is written as rules that the server checks on every request. Hiding a button is never the only protection.
Tests before every save
Each build runs checks, including tests that sign in as different users and try to read or change records they shouldn't. A build is only saved as a version when they pass.
A Security tab you can read
Every rule in plain English, warnings for risky ones (like anyone being able to delete orders), and a one-click plan to fix them.
Keys stay on the server
API keys and payment secrets are encrypted and write-only: you can replace them, not read them back. A scan flags keys pasted into the app's code.
Preview and live are separate
You build and test with sample data. Customers only ever see the live app, with its own database.
Payments verified on the server
An order is only marked paid after the server confirms the payment with Razorpay or PayPal, not because the browser said so.
Data, access and publishing.
Real database
Every app gets its own database. Browse and edit live and preview records in the Database tab.
Copy preview data to live
When you publish, you can copy the preview's sample records and files into the live app.
Rules enforced on the server
Who can see, add, edit or delete each record is checked by the server on every request, so screens cannot get around it.
Tests on every build
Each build runs checks, including access-rule tests, and is only saved when they pass.
Security tab
Shows who can do what in plain English, flags risky rules, and offers a one-click fix plan.
Leaked key scan
Flags passwords or API keys written into the app's code and suggests moving them to the server.
Admin panel at /admin
Every app comes with an admin panel for records, users, CSV export and files.
Users and roles
App admins can list users, change roles and block people. The last admin cannot be removed by mistake.
Sign-up modes
Choose open sign-up, sign-up with admin approval, or invite only.
File uploads
Apps can store uploaded files privately. Up to 25 MB per file and 200 MB of data per app.
New-record alerts
App admins get notified when new records come in, like orders or bookings.
One-click publish
Publish to a live web address like yourshop.app.make27.com, with real data and real sign-ins. Re-publishing an app that is already live is always allowed.
Separate preview and live data
The preview uses sample data. Your customers only ever see the live app.
Nothing is deleted
If a paid plan lapses, live apps stay online 7 more days, then pause until you pick a plan again. Apps and data are never deleted.
Custom domains
Use your own domain for a published app instead of the app.make27.com address.
Code export and GitHub
Download your app's code or push it to GitHub.
Found a security problem in make27 or an app built with it? Email us through the contact page. See the privacy policy for what we store.
make27 Studio
Describe it in one message. See it running today.
Your first app is free. A typical first build uses about 160 of the 500 credits you get. No card needed to start.